OwlAudit
OwlAudit provides Hash Chain audit ledgers and policy-driven HITL / HOTL / HOOL three-tier interventions. Human review tickets support pending states, escalations, timeout fallbacks, and decision provenance. Synchronous evaluation runs on connected NodalOS hooks; generic ingest logs records without blocking past executions.


OwlAudit
Compliance Audit & HITLAI Agent compliance audit and human-in-the-loop (HITL) governanceCommitted actions are verifiable and traceable; on connected NodalOS hooks, policy-triggered high-risk actions await human sign-off.
- Verifiable
- Recompute hashes and detect gaps on committed chains
- Real-Time Blocking
- Synchronously rejects actions matching HITL policies on NodalOS hooks
- Three Tiers
- HITL · HOTL · HOOL
Typical pains
- Agents call production APIs directly without human oversight or guardrails
- Post-incident forensics lack complete, tamper-evident audit trails
- Compliance policies fail to translate into concrete Agent behaviors
Core value
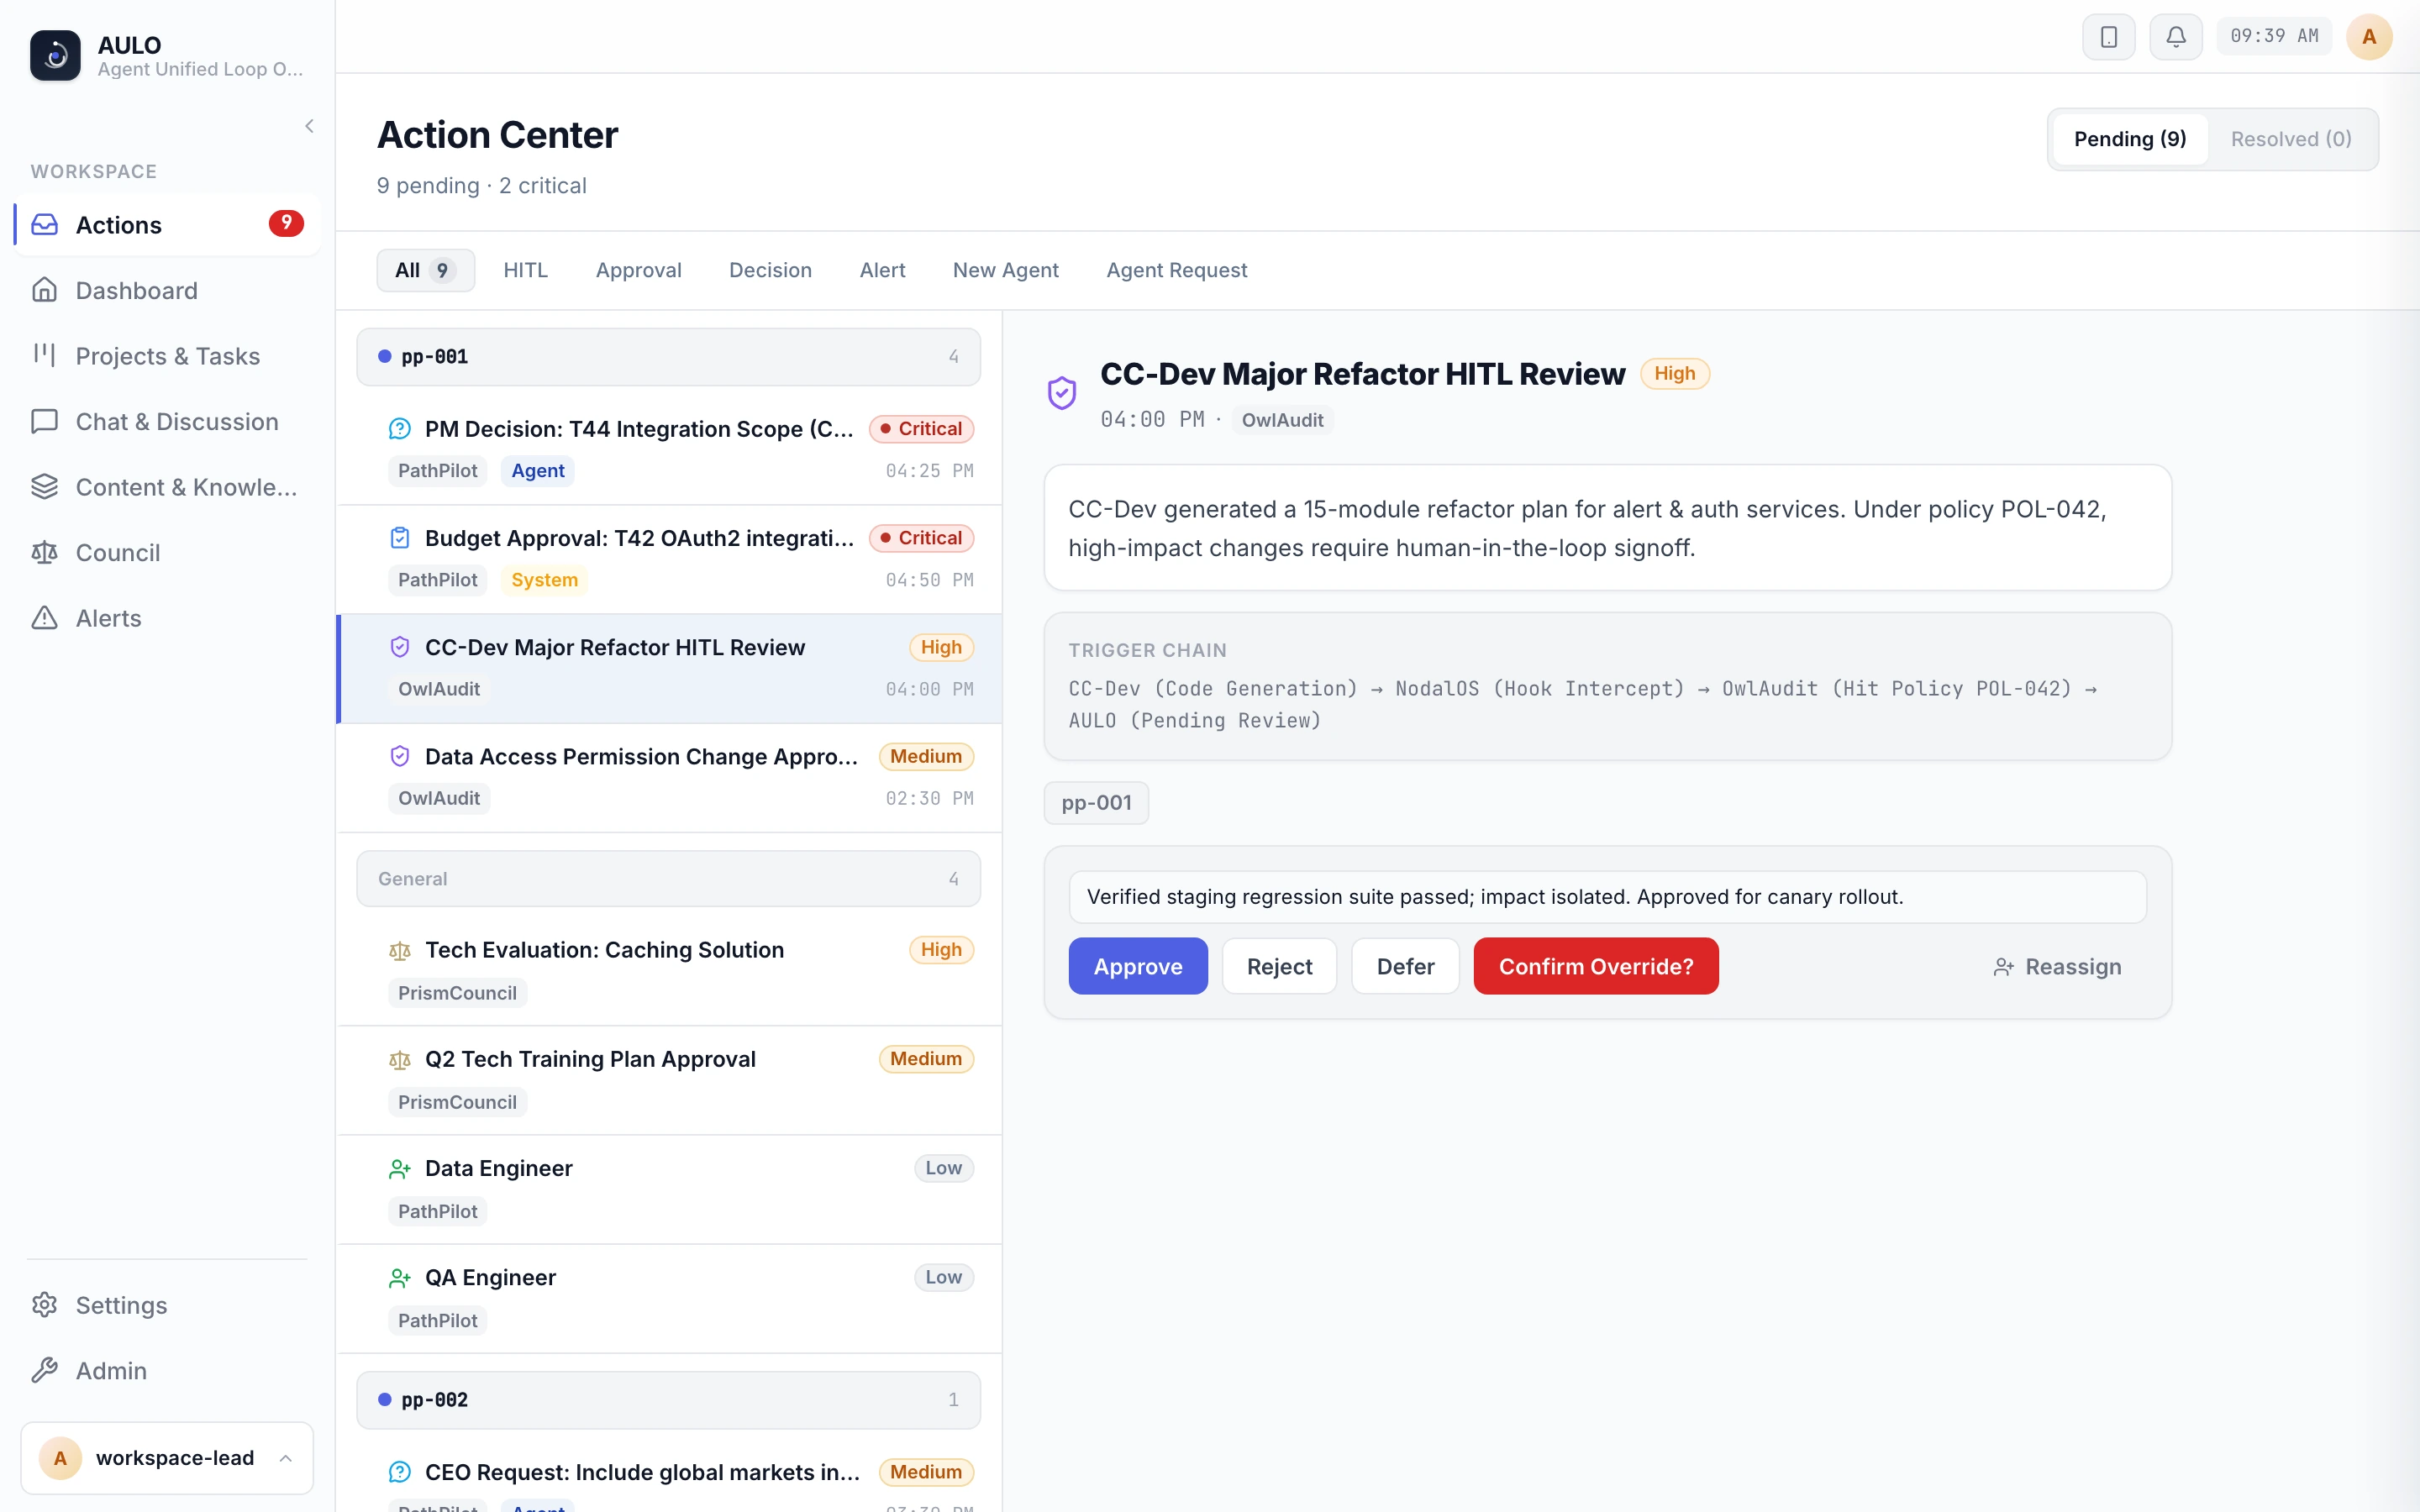
Gate high-risk actions behind human approval
Critical agent actions need a human check. On connected NodalOS hooks, actions matching HITL policies are rejected and opened as review tickets, proceeding only after approval. Sign-off happens in AULO and is written back upstream; timed-out tickets escalate to the next approver.
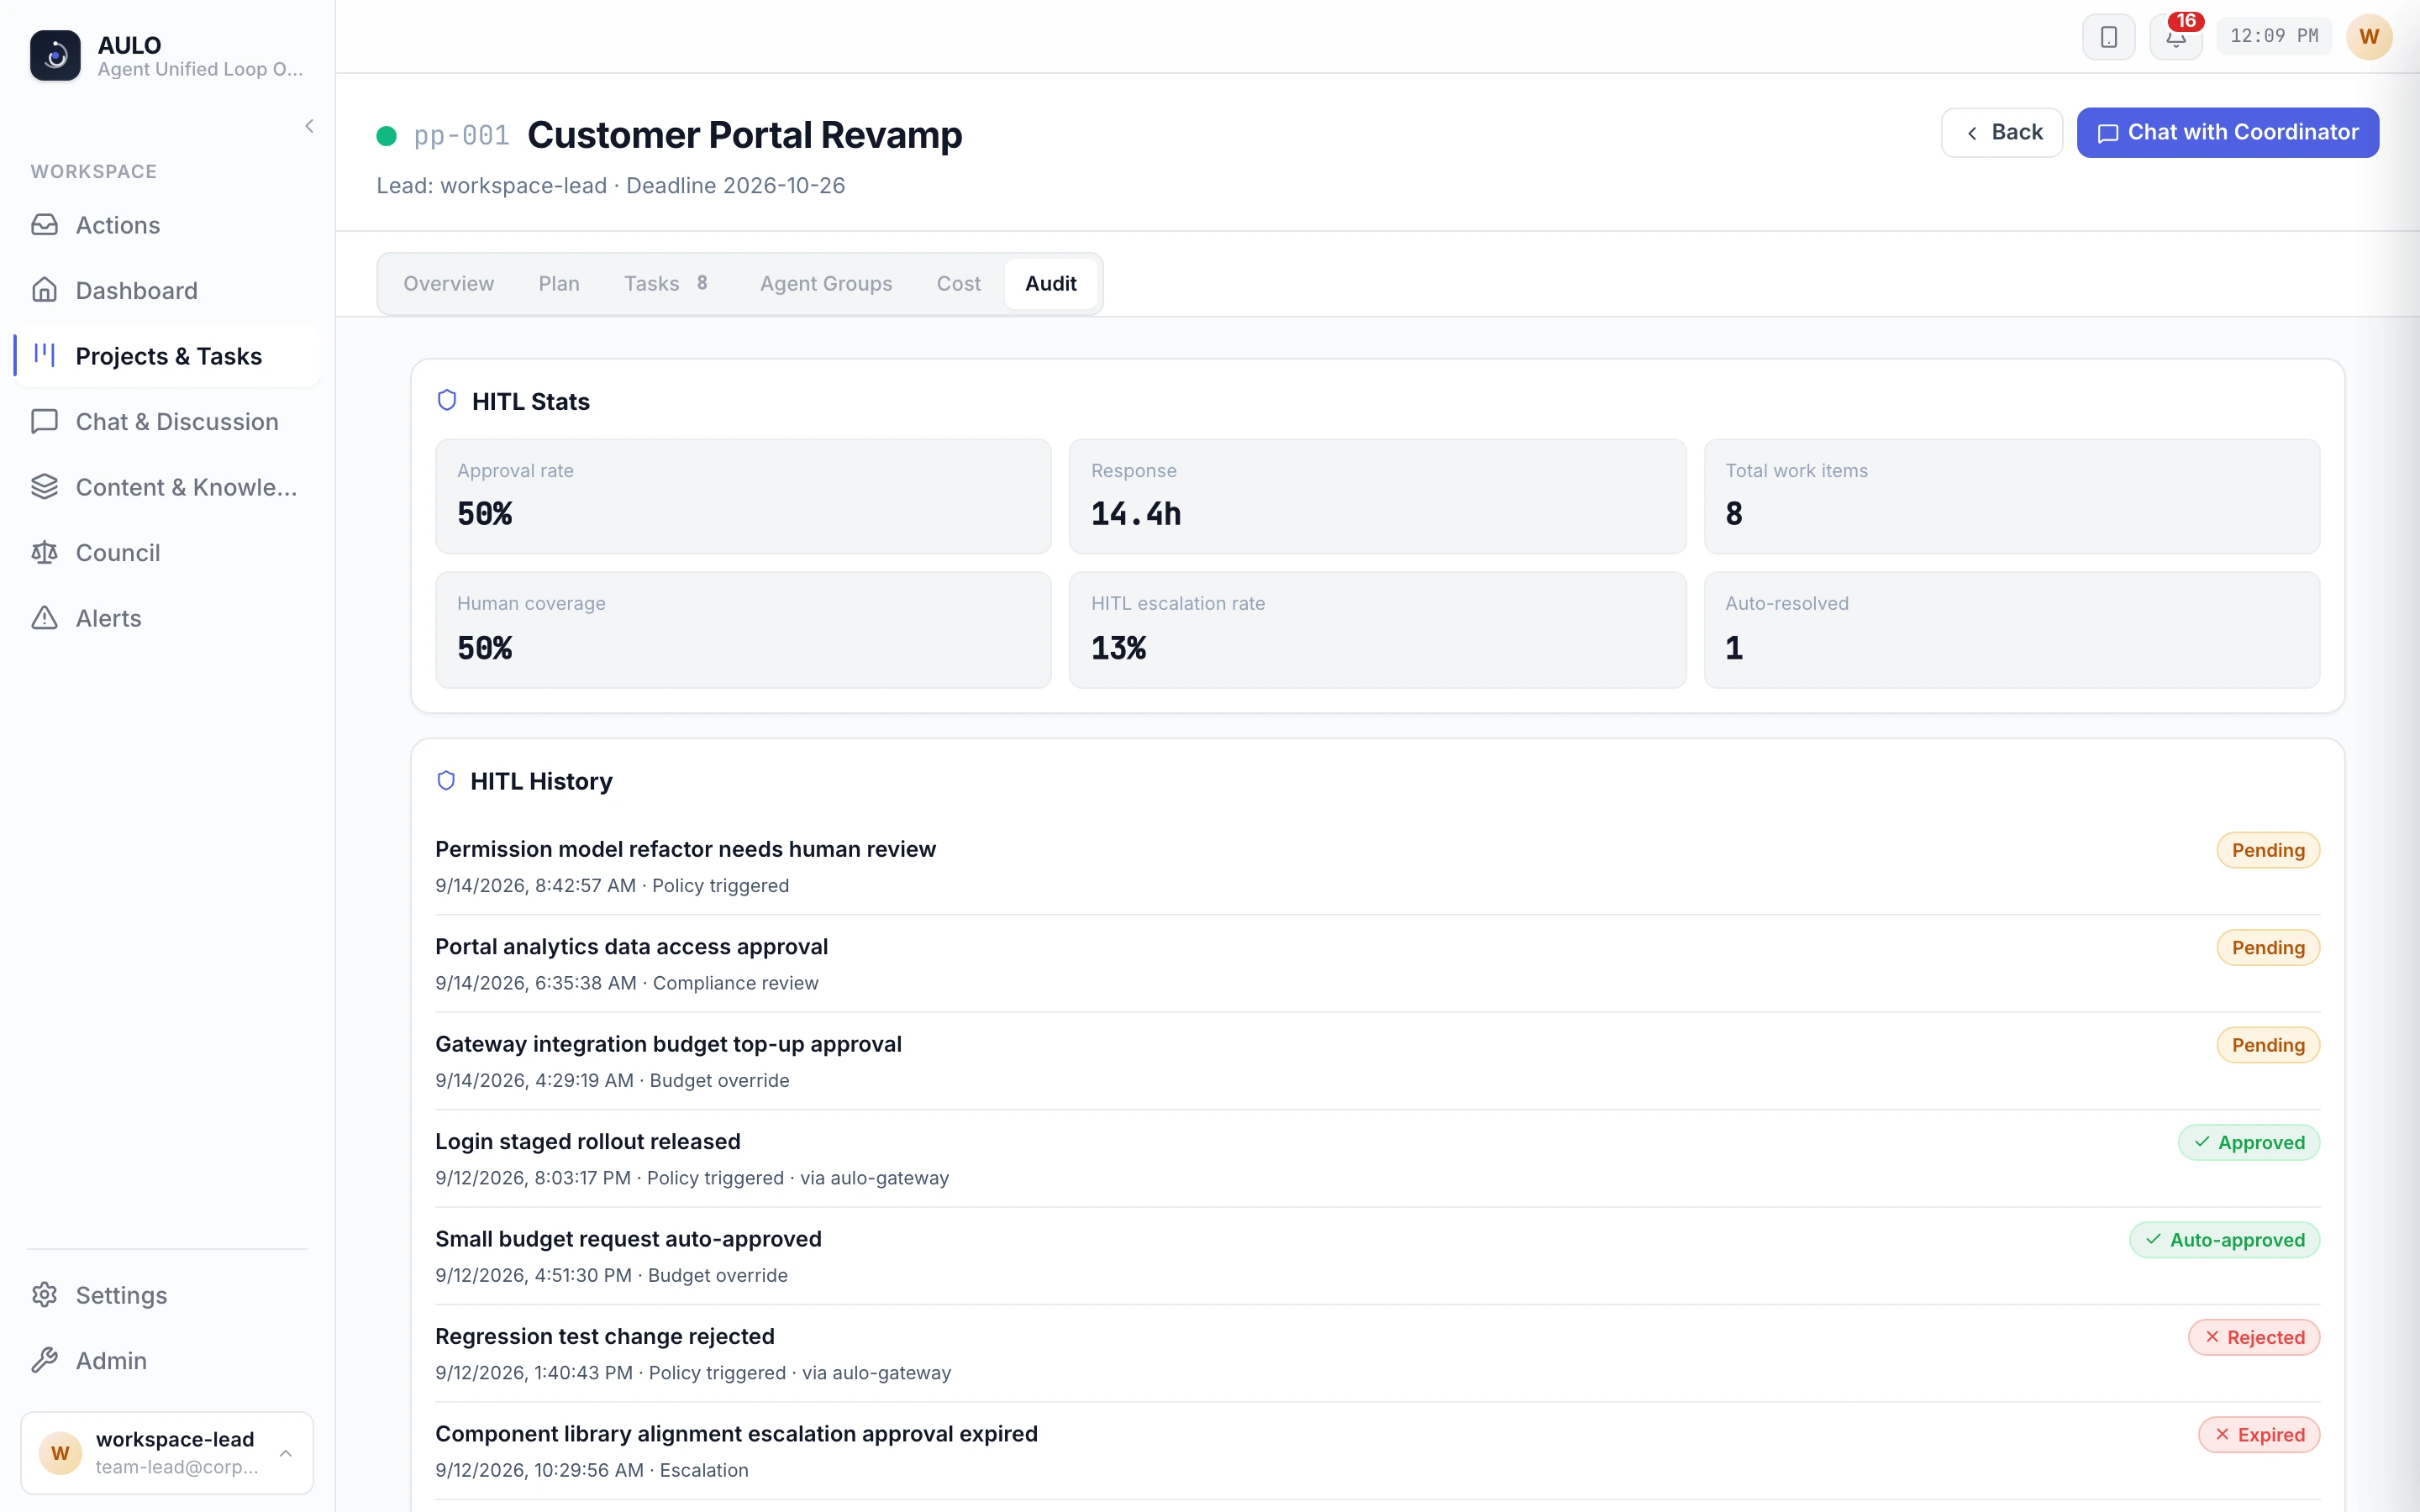
Track review workload and human coverage by project
Without project-level metrics, teams cannot gauge human review bottlenecks or audit rigor. OwlAudit tracks approval rates, resolution times, event-based human coverage, and escalation rates per project, listing ticket categories and outcomes on the AULO audit page.
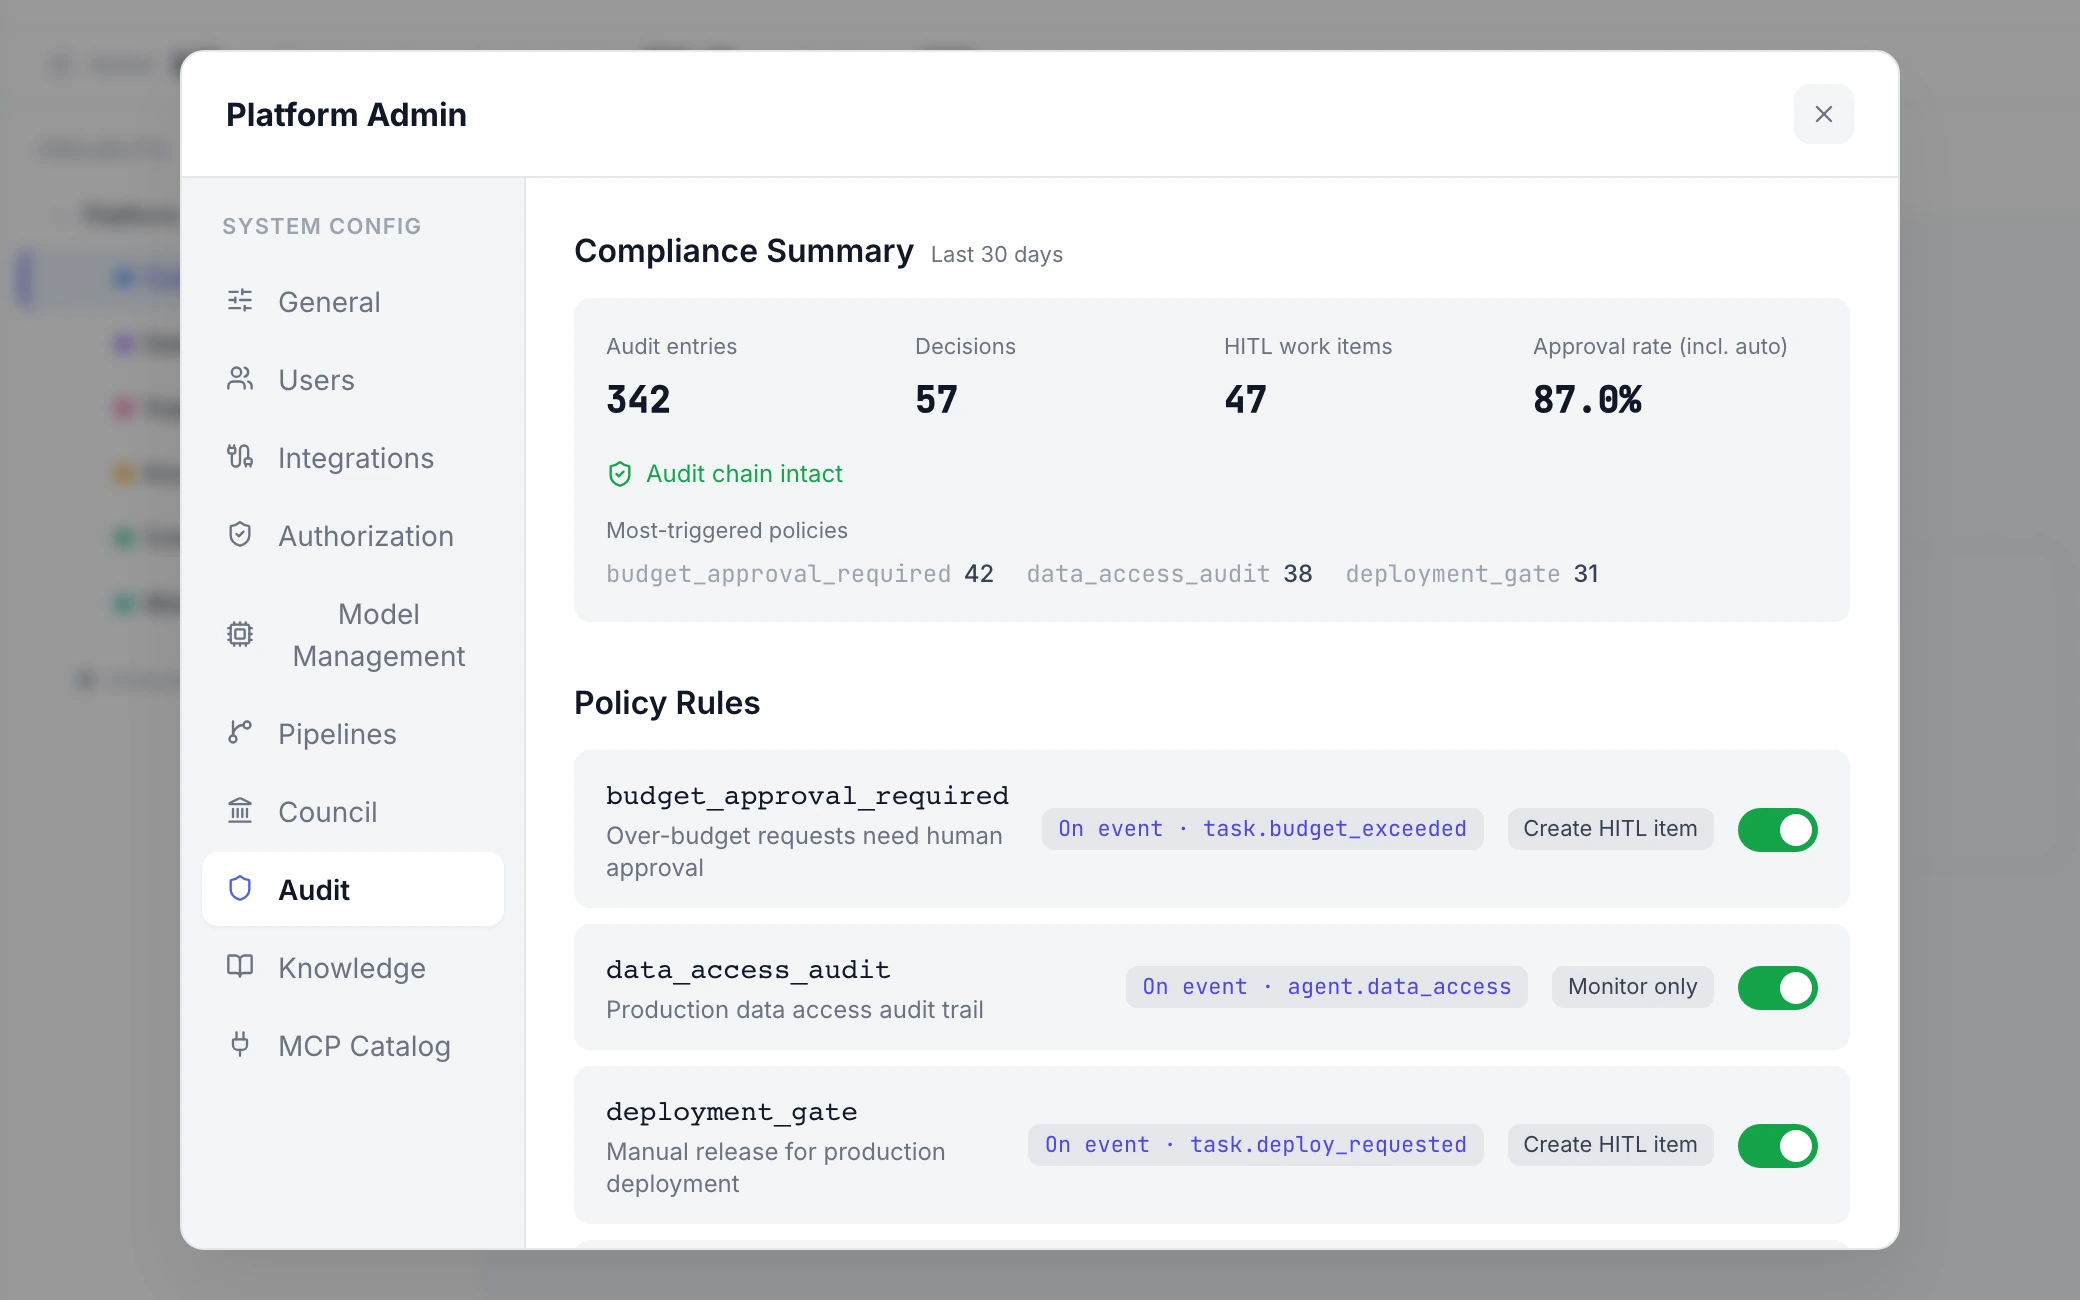
Inspect compliance posture and configure audit policies in AULO
Compliance teams need continuous visibility into audit postures and the ability to adjust audit policies as needed without touching agent code. AULO displays compliance summaries and HITL metrics and exports reports; create, edit, toggle, or delete event policies in AULO with trigger records and revision history, evaluated by OwlAudit.
Capabilities
Audit ledger
Human-in-the-loop
Policy & freeze
Reporting & integration
Does / does not
- Verifiable Hash Chain audit ledger: recompute, verify, and detect chain gaps
- Three-tier HITL / HOTL / HOOL intervention: policy-driven human-in-the-loop gates
- Policy dual-version provenance: policy changes and audit records increment versions in the same transaction
- Human review ticket lifecycle: pending, escalation, timeout fallback, and decision provenance
- Compliance freeze and real-time blocking: synchronous deny and freeze on connected NodalOS hooks
- Objective audit reporting and veto metrics: compliance summaries and objective stats for AULO
- Does not replace professional legal and compliance advisory
- Does not perform subjective black-box scoring (records facts and human veto rates, not unexplained scores)
- Does not replace existing enterprise GRC / SIEM suites (focuses on Agent runtime control and in-product compliance reports)
- Does not perform physical off-chain real-world investigation (verifies integrity of records already written to the ledger)
By role
Works with NodalOS hook policy evaluation to reject and log high-risk actions
Provides a complete loop across reviews, escalations, and audit trails rather than mere pre-call blocking; tracks review veto frequency for governance
On connected hooks, policy-triggered HITL actions are blocked synchronously pending sign-off